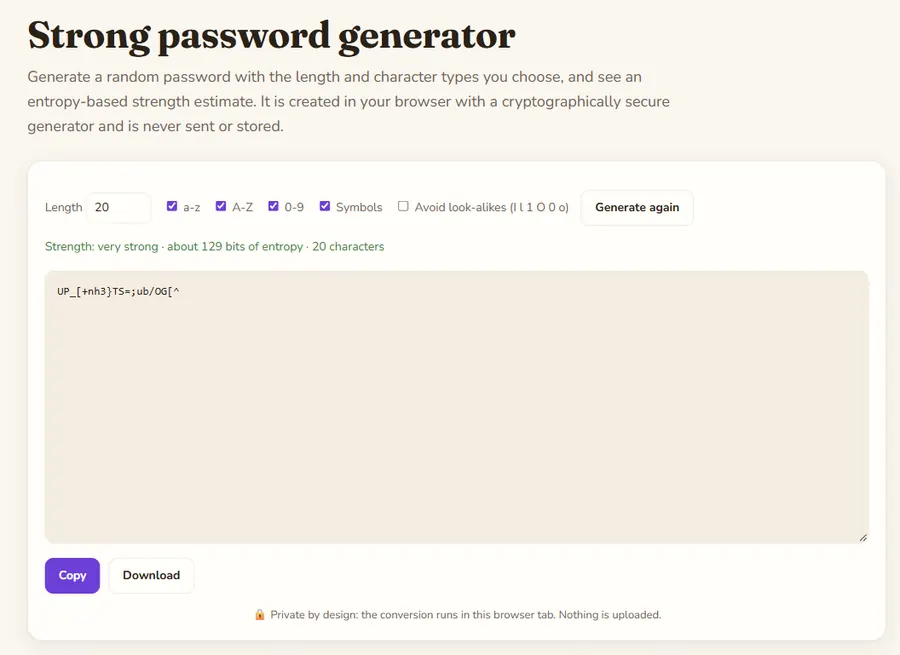
Generate a random password with the length and character types you choose, and see an entropy-based strength estimate. It is created in your browser with a cryptographically secure generator and is never sent or stored.
Strong password generator is a free online tool by Hack the Hydra. Create strong random passwords of any length with your choice of letters, digits and symbols. Made in your browser with a secure random generator; never sent or stored.
How the password is made
Each character is picked with crypto.getRandomValues(), the same secure random source browsers use for encryption keys, using rejection sampling so no character is more likely than another. If you tick several character types, the password is guaranteed to contain at least one of each, then shuffled so those characters are not always at the start. Nothing is sent over the network and nothing is saved: close the tab and it is gone.
Length beats complexity
Each extra character multiplies the number of possibilities, so length matters more than symbols. A 20-character password using all four sets has about 128 bits of entropy, far beyond what can be guessed offline. Use at least 14 characters for ordinary accounts and 20 or more for your password manager's master password or anything that protects money. The strength label is calculated from length and pool size and assumes the attacker knows the rules you used.
Using it safely
Use a different password for every site and store them in a password manager rather than reusing a memorable one. Turn on two-factor authentication where available. If a site rejects some symbols, untick "Symbols" and add a few characters of length. On a shared or public computer, clear the clipboard afterwards.
How to use
- Choose your options.
- A new result is generated every time you change an option, or click "Generate again".
- Copy the result or download it.
FAQ
Is the password sent or stored anywhere?
No. It exists only in this page, generated by your browser. We do not receive it, and the page does not save it.
Are the passwords truly random?
They use crypto.getRandomValues(), a cryptographically secure source, not Math.random(). The selection avoids modulo bias.
What does the strength estimate mean?
It is entropy in bits: length times log2 of the number of possible characters. Under 40 bits is weak, 40-59 fair, 60-79 strong, 80 and above very strong.
Why avoid look-alike characters?
I, l, 1, O, 0 and o are easy to confuse when you must type a password from a screen or paper. Excluding them reduces the pool slightly, so add a character or two of length.
 Hack the Hydra